Pearl
 Zylo Ecosystem
 Bitway
 Walrus
 Starknet
 Quantus
 Pudgy Penguins

Attacker-linked wallets from the Bitget hack used THORChain while moving stolen assets across blockchains. Bitget has asked the protocol to refuse transactions from identified addresses, but THORChain defended its permissionless architecture.
Bitget now estimates approximately $387.5 million reached attacker-controlled addresses during the Sept. 24 incident. The exchange initially placed the affected amount at $351.6 million.
Bitget Hacker Is Exploiting THORChain to Convert User Funds
On-chain data shows that the hacker behind the $351 million Bitget hack is exploiting THORChain. Data from Arkham Intelligence shows that the hacker address, reportedly the notorious North Korean Lazarus Group, has swept Ethereum (ETH) for Bitcoin (BTC).
As reported earlier, the hacker had stolen 34,890 ETH worth $85 million from the exchange. This is the second-biggest crypto asset after XRP, in value terms, stolen from Bitget.
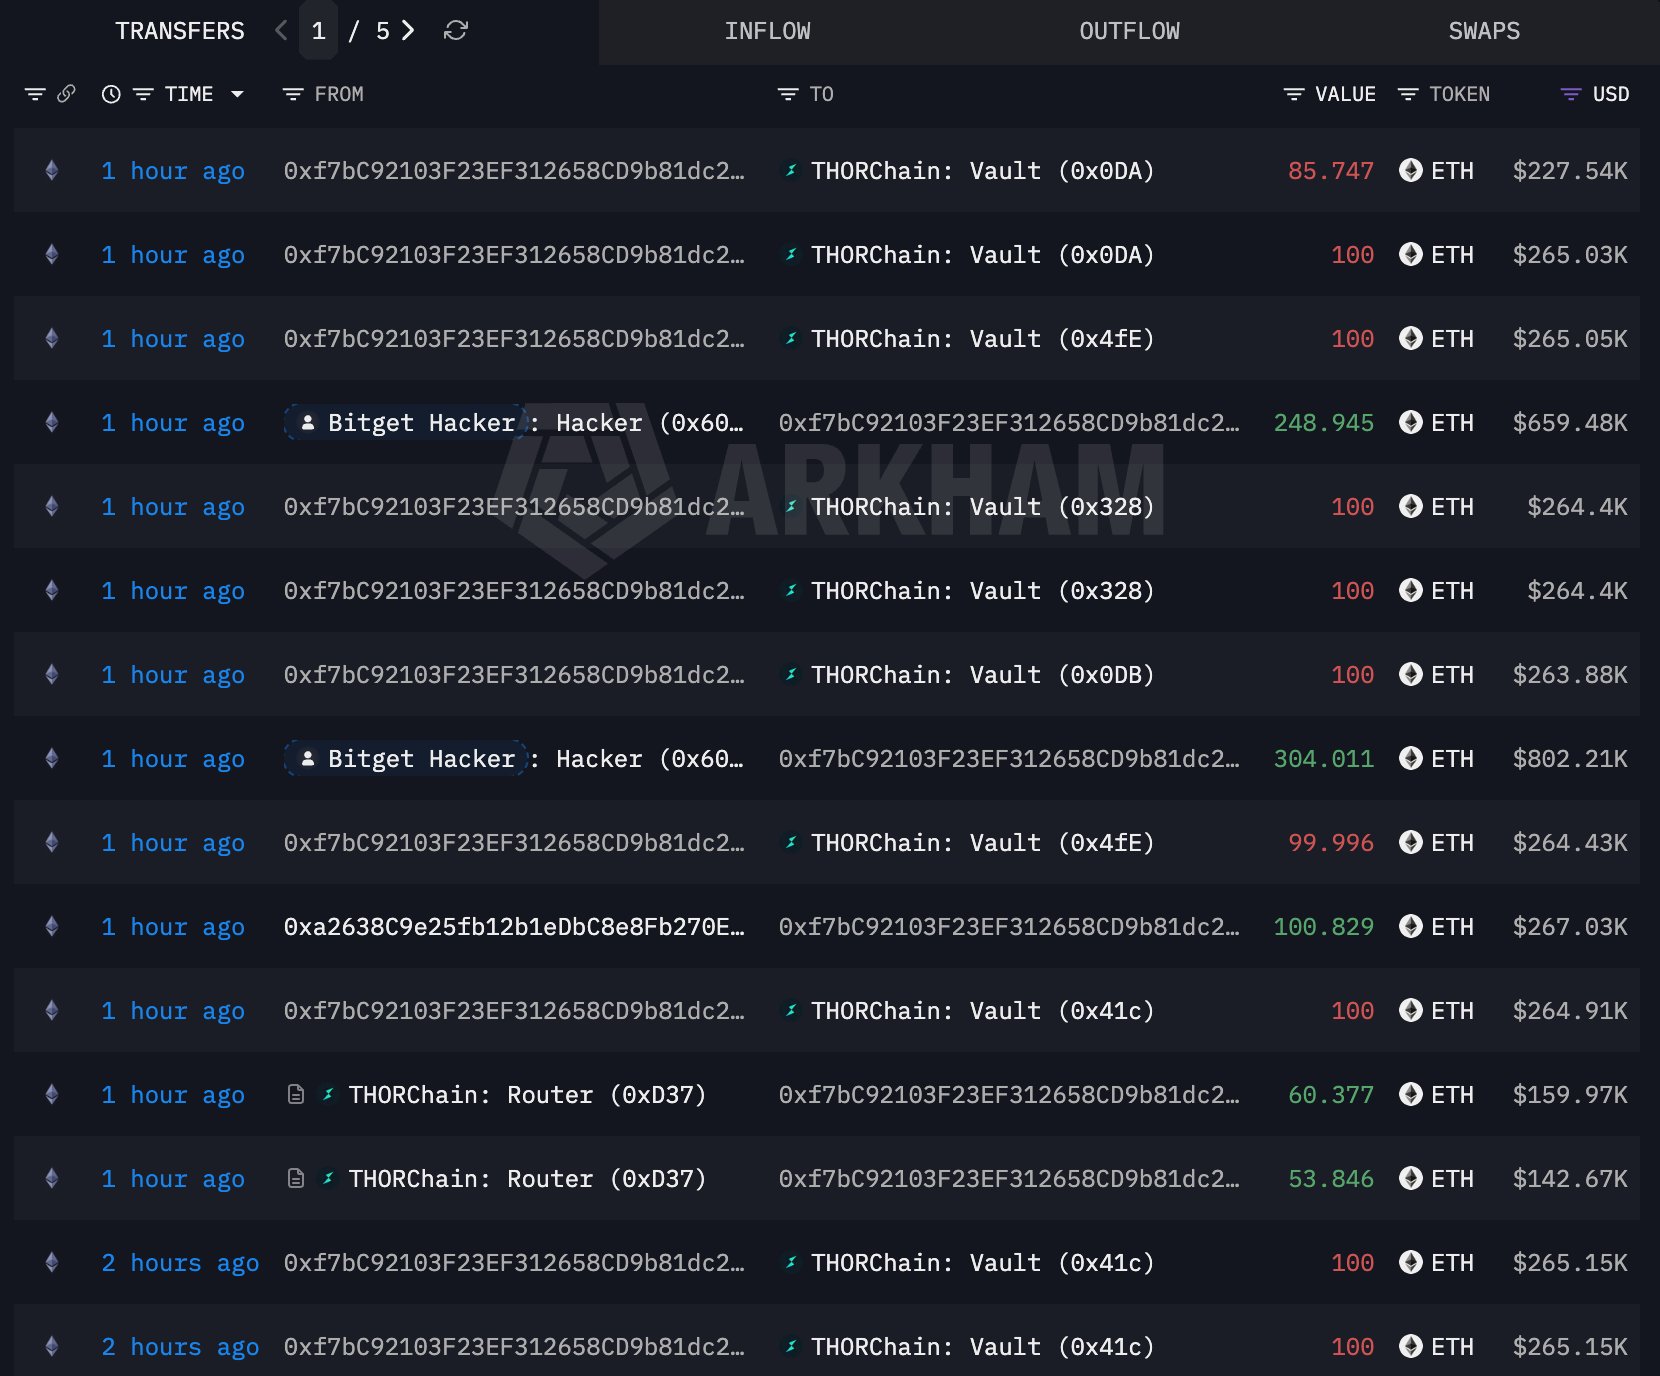
On Friday, September 25, MistTrack reported that the hacker is misusing the THORChain platform to get away after the theft via asset swaps and cross-chain transfers. “After the $1.46B Bybit hack last year, nearly $1.2B in stolen funds was reportedly traced through THORChain, as the attackers moved assets across chain,” they noted.
The attacker-linked addresses have been publicly identified and are being actively monitored by exchanges, blockchain security, and AML firms. MistTrack noted that THORChain needs to take responsibility and should not become a go-to platform for attackers to swap assets.
Speaking on this development, BitGet CEO Gracy Chen noted: “Our attacker addresses are publicly listed and actively tracked. We are formally asking THORChain to refuse service to these addresses. Decentralization is a design principle, not a shield for facilitating known stolen funds. The industry is watching.”
THORChain Defends Its Stance on Not Blocking Hacker Addresses
THORChain said network halts are emergency security mechanisms designed to protect the protocol. It added that they cannot be used as tools to selectively freeze specific funds or block individual swaps.
The protocol cited a May 2026 exploit that resulted in $10.7 million being stolen from liquidity pools. THORChain said the attackers’ addresses were not blacklisted during the incident and therefore were not prevented from swapping on the network.
“THORChain is permissionless and doesn’t censor by design,” it added in a mesage on the X platform.
Some of the industry people have also come in support of THORChain, regarding its latest stance. Digital nomad Michael Perkins wrote: “All tools in existence are inherently neutral by nature. It is the man who wields the tool that decides whether they will use it for good or for bad, and you cannot blame tools for the actions of men”.
Bitget Resumes Bitcoin Withdrawals
Accroding to the scheduled timeline, crypto exchange Bitget has resumed withdrawals on its platform starting today, September 28. The exchange said the vulnerability has been remediated, no further unauthorized transfers have been identified since the incident was contained.
Moreover, it added that the user funds remain unaffected. CEO Gracy Chen previously said Bitget plans to replenish its Protection Fund to its $300 million baseline within a week.
As reported by X Handle “Ai”, Bitget has transferred 2,042.28 BTC, worth approximately $169 million, from its roughly 5,500 BTC Protection Fund to hot wallets. Moreover, another 3,457.72 BTC remains on-chain.
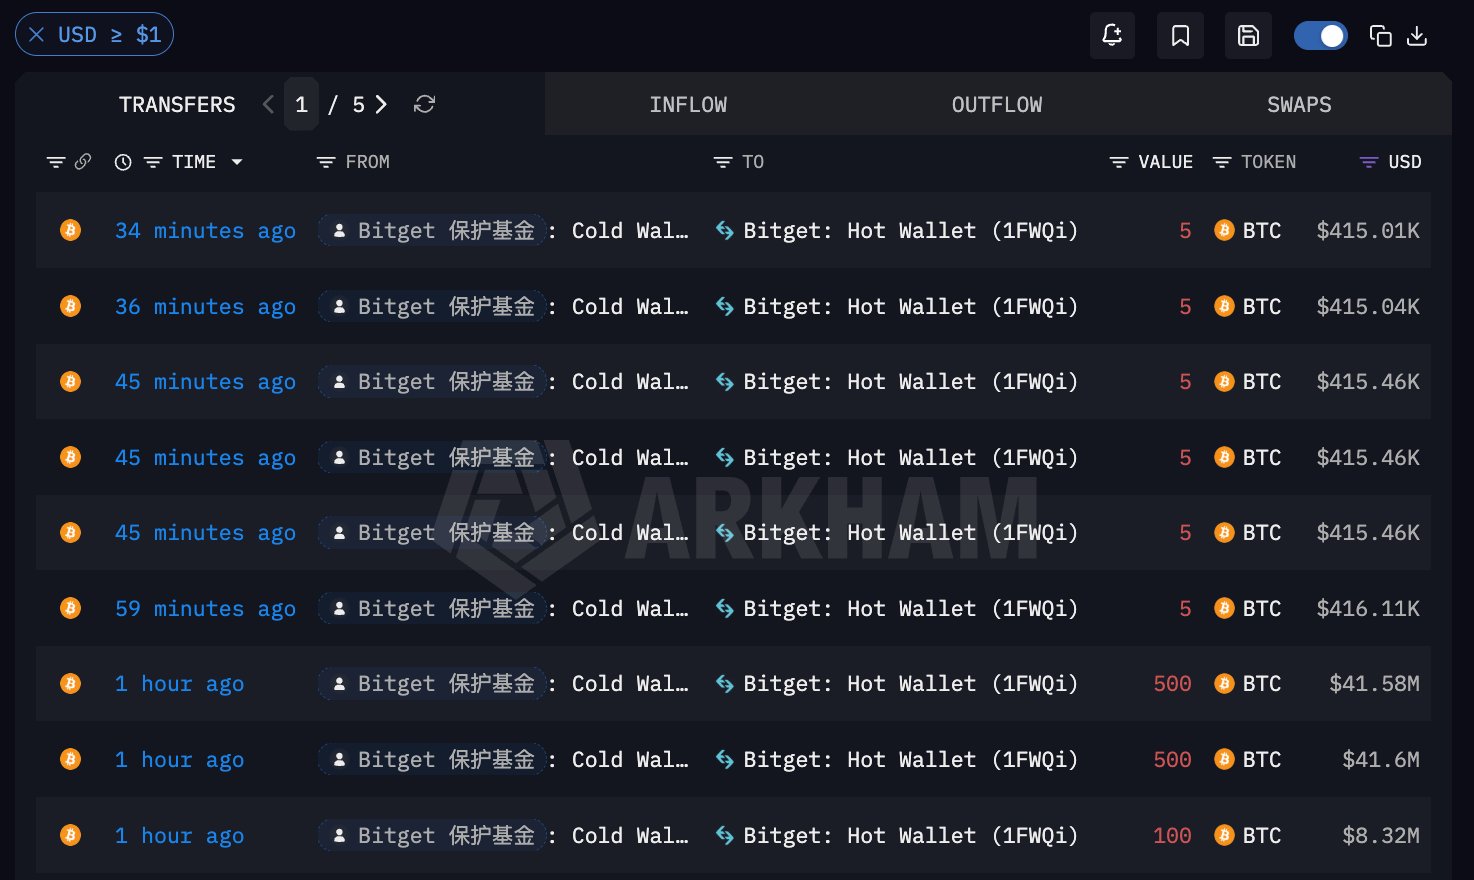
She noted that the transfers were made in advance and should not be interpreted as actual user withdrawal activity
This article is for informational purposes only. Blockchain labels and analytics do not independently establish the identity of wallet controllers.