astronaut
 Zylo Ecosystem
 Pearl
 Bitcoin
 Quantus
 Pudgy Penguins
 Bitway

An Ethereum phishing attack reportedly drained 1,010 ETH from a user who accessed a Tornado Cash-linked website. WuBlockchain cited community reports claiming the victim reached a fraudulent frontend through an old tornado.cash link.
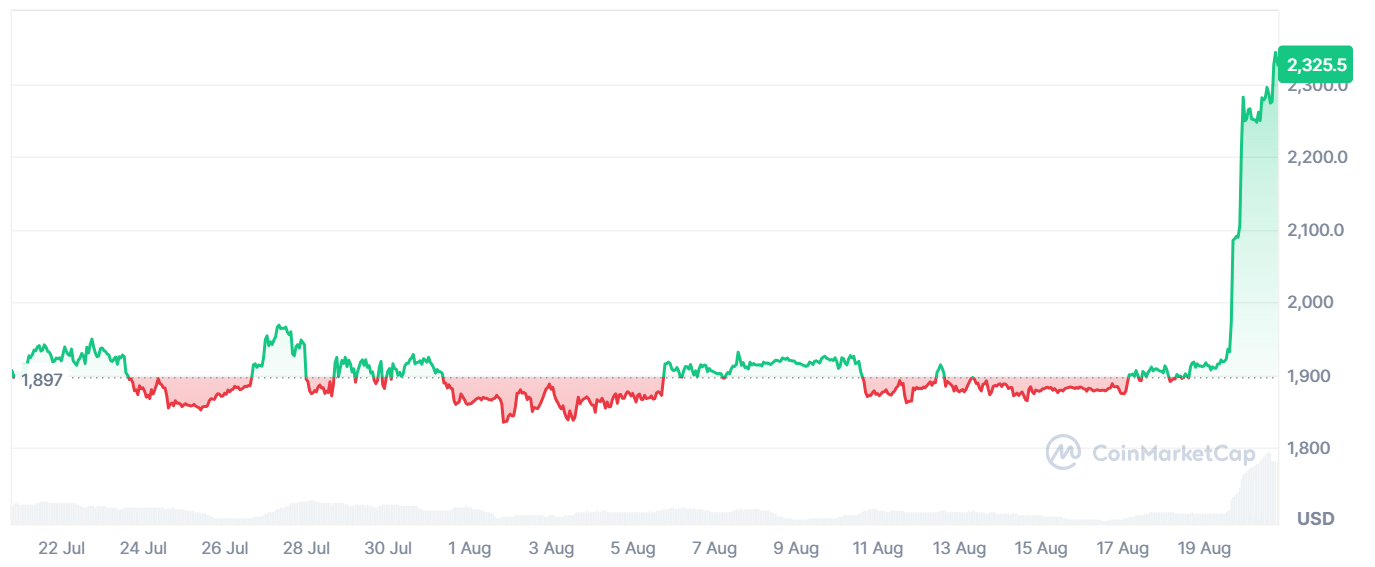
The reported loss was worth roughly $2.3 million as Ethereum traded above $2,200. However, separate reports disputed both the exact amount stolen and claims that attackers had taken control of Tornado Cash’s former domain.
Onchain Analyst Questions Phishing Victim Background as Ethereum Crosses $2,000
The incident comes at a time when Ethereum is enjoying a positive performance with the flagship token climbing above $2,300. This meant the victim lost well over $2.3 million in the phishing incident.
So far, there are no signs that the attacker has moved the stolen funds out of their addresses. The phishing also appears to have used similar techniques to steal up to $4 million in the past 12 months.
While the incident has garnered reactions from several crypto users, the phishing victim has also come under scrutiny. Onchain investigator Specter noted that the victim might be a threat actor.
In a reaction to on X, Specter stated that the original 73 Bitcoin came from a Whirlpool mixer two weeks ago, with part of it bridged to Ethereum. According to the pseudonymous investigator, it is strange that the victim used two mixers to avoid a compromise of a hardware wallet.
They added that the victim was also seen in private-key-finder and brute-force Telegram groups, which further supports the theory that they might be a threat actor.
Crypto Threat Actors Relying on Fake and Hacked Websites for Phishing Attacks
Meanwhile, the incident is part of a growing trend of threat actors using fake or hacked websites to target crypto users. According to a report by Malwarebytes, scammers are using fake anti-money laundering services to drain users’ wallets.
These services allow a user to check whether a crypto wallet has interacted with illicit or stolen funds. However, scammers are cloning legitimate platforms or creating fake ones with generic names that require users to connect their wallets to complete the checks.
Interestingly, another report by Check Point Research revealed that bad actors hacked nearly 2,000 WordPress sites to steal crypto wallets and spread malware.
The report noted that the operation is part of the StopAndProtect ransomware attack, with hackers deploying malware on hacked websites.
Users who visit compromised websites are targeted by a fake CAPTCHA that prompts them to run a command that installs malware on their computer. The malware steals private credentials, including wallet seed phrases, and can spread through the network and USB drives.
According to Check Point researchers, the entire infrastructure can even lock the screen of infected devices and deploy ransomware.